Cryptography · Post-quantum · Supervision
Vorwarnzeit
(Warning time) How cryptographic algorithms age, break and are replaced
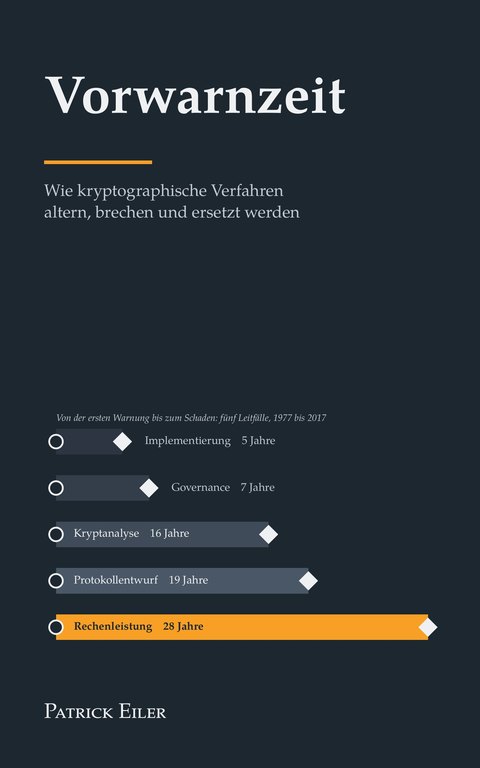
How long does an algorithm warn before it breaks – and who listens? Cryptographic algorithms rarely fail overnight. For thirty years of cryptography this book measures the time between the first reliable warning and the damage – for DES, MD5, SHA-1, RC4, Bleichenbacher's attack, ROCA and Dual_EC_DRBG. Where there was a publicly observable precursor, the gap averaged twenty-one years. Action was mostly taken only once the weakness could no longer be overlooked.
This raises the question for the present. The migration to quantum-safe algorithms is meant to succeed within eleven years, faster than any migration observed so far. The book assesses quantum computers, artificial intelligence, standardisation and roadmaps, examines certification and supervision under DORA, NIS-2, the Cyber Resilience Act and eIDAS, and proposes a simple, verifiable metric.
Among other things, the book covers:
- Five patterns of breakage: computing power, cryptanalysis, protocol design, implementation and side channels, governance
- What is in use today: the symmetric and asymmetric stock, current protocols, hardware-based mechanisms
- Today's attack surface: quantum computers, artificial intelligence, classical cryptanalysis against young algorithms, implementation and supply chain
- The transition: standardisation, roadmaps and where the migration actually stands
- Who actually checks? Certification schemes, the regulatory framework and the gap between assessment and reality
- The algorithms in detail and a timeline of cryptographic breaks from 1993 to 2026
For anyone in institutions, audit firms or supervision who plans, steers or reviews the migration to quantum-safe cryptography.
- Edition
- Paperback and Kindle e-book
- Length
- 438 pages
- Language
- German
- Published
- 1 November 2026
- ISBN (paperback)
- 979-8166868442
- Status
- data and legal status as of 29 October 2026